

Cybersecurity for accounting firms.
Protection for client financial information, seasonal staff access and business systems, with routine maintenance planned around filing deadlines.
Rather not book now? Leave your email and we'll get in touch.
We reply within 24 hours. Privacy policy
Send a message or email hello@teclara.tech
Security through the filing cycle
Seasonal staff, heavier document volumes and filing deadlines all put pressure on access and recovery. Permissions and backups are checked before the busy period starts.
January
Seasonal preparers start
Each seasonal preparer gets an individual account with access to their assigned client files and an end date set in advance.
February to April
Client documents arrive by email
Staff receive tax slips, statements, and identification documents through email attachments and links. Email filtering and sign-in monitoring help detect phishing attempts that impersonate clients or the CRA.
April 30 and June 15
Filing deadlines approach
An outage near a filing deadline can stop client work. Routine updates and recovery tests are scheduled around the practice’s busiest weeks.
May onward
Seasonal staff finish their work
Post-filing reviews cover seasonal accounts and shared client folders. Access that is no longer needed is removed.
Client access and offboarding
Shared links and permissions tend to linger after seasonal staff leave or client work closes. Regular reviews find them, and anything no longer needed is removed with your approval.
Access
Client files stay with the assigned team
Client-folder access in Microsoft 365 or Google Workspace is limited to the people working on that client. Closeout reviews catch shared links and permissions that are still open.
Sign-in
Named-account protection
Multi-factor authentication (MFA), administrator controls and sign-in policies protect staff accounts. Shared mailboxes are opened through each person’s own account, so access can be reviewed and removed one person at a time.
Devices
Device security for client work
Supported computers receive managed endpoint protection, encryption, and security updates. The security team reviews alerts, investigates suspicious activity, and coordinates the response.
Email
Impersonation and payment-fraud protection
Email controls filter common phishing and impersonation attempts. Stronger protection for email sent from the practice’s domain, and a payment-change procedure, can be added if the practice needs them.
Calendar
Maintenance around filing deadlines
Patching, configuration changes and planned maintenance run on a schedule set with the practice, around filing deadlines.
Recovery
Backup coverage and recovery
Microsoft 365 or Google Workspace is backed up every day to a separate location, and restores are tested.
Evidence for client and insurer reviews
When a client, insurer or practice inspector asks how information is protected, current records of the security work are ready to share.
- Cyber insurer, at renewal
- Is MFA enforced on email and remote access? Are backups kept separate and tested?
- Current MFA and sign-in policy reports, what the backup includes, and the date and result of the last restore test.
- Business clients
- How are our financial records protected, and who at your firm can open them?
- A plain description of the protections, with access limited to each client’s team and reviewed when the work closes.
- Practice inspector for assurance firms
- How does the firm manage the technology its quality management system relies on?
- Records of patching, access reviews, backup, and monitoring for the managed systems, which the firm can reference in its CSQM 1 documentation.
Security for business systems
Protection for Microsoft 365 and Google Workspace, set up around how your practice shares information and who needs access to it.
On Microsoft 365
- SharePoint and OneDrive client folders with permissions based on each person’s role
- MFA, Conditional Access, and administrator access controls
- Managed endpoint protection on supported devices
- Update schedules planned around filing deadlines
On Google Workspace
- Shared drives with permissions based on each person’s role
- Gmail phishing and impersonation protection
- External sharing links reviewed when work closes
- Google Vault aligned with retention policy where licensed
Settings are kept up to date as part of the service, and upgrades to the tools and monitoring you already have come at no extra cost.
Frequently asked questions.
How does the service support insurance applications and renewals?
Insurance reviews use current evidence of sign-in controls, device protection, monitoring and backups. Every insurer and policy is different, so the evidence supports the application but can’t guarantee approval or coverage.
What support is available during filing season?
With Managed Security & Compliance, people on the security team review alerts around the clock and respond to real threats. Day-to-day user support and administration come with Managed IT, which includes Managed Security & Compliance. Planned changes are scheduled around known filing deadlines.
Can the service complement or replace an existing provider?
Yes. Managed Security & Compliance can work alongside your current provider. The handover starts with a record of the current setup and who does what, and the switch is timed around the practice’s deadlines. Managed IT adds user support, device administration, onboarding and platform management, with Managed Security & Compliance included.
What documentation is available?
Reports can include sign-in and access records, backup and restore evidence, patching and vulnerability status, alert response records and written descriptions of each control, all for the systems Teclara looks after. The documentation supports client, insurance or professional reviews but doesn’t replace legal or accounting advice.
Are Microsoft 365 and Google Workspace both supported?
Yes. Both platforms are covered for accounts, administrators, email, sharing, devices and backup. Some controls depend on your licence, so current licences are checked before setup starts.
What isn’t included?
The practice decides how long records are kept and which professional, privacy and tax rules apply. CRA portals, tax applications, workstations, file servers and local working papers stay with the practice or its software provider unless backup, recovery or administration for them is added.
What a client says about working with us.
“Teclara materially improved both our operational responsiveness and our security posture.”
E.C.
Senior Leadership, GTA Consulting Firm
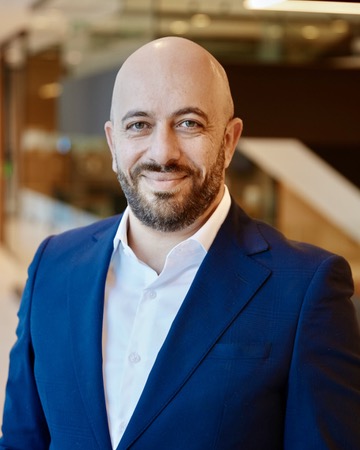
Led by Wadhah Hussain, Teclara's founder
Enterprise Architect · 20+ years in enterprise IT, including OMERS, Accenture, Deloitte and Slalom
Based in Oakville, serving Canada remotely, excluding Quebec.
Work is delivered remotely from Oakville, and there are no offices in the other listed areas.
Your practice’s security, looked after.
Before the next filing season is a good time for a 15-minute call about access, backups and email.