

Cybersecurity for consulting firms.
Protection for confidential client work, project-by-project access and remote devices, with records ready for client security reviews.
Rather not book now? Leave your email and we'll get in touch.
We reply within 24 hours. Privacy policy
Send a message or email hello@teclara.tech
Access across changing project teams
Specialists and project teams need access for a defined piece of work. Account and sharing reviews keep up as people join, leave and projects close.
Proposal
The questionnaire comes with the RFP
Client procurement often asks for evidence of security controls. Records of the protections Teclara runs make those answers easier to back up.
Kickoff
Access is granted in both directions
Consultants may work in client systems while sharing files from the firm’s own environment. Associates and subcontractors get individual accounts with permissions set for their role.
Delivery
Work happens away from the office
Consultants use the same accounts and devices at client sites, on the road and at home, so device protection and sign-in controls go with them.
Closeout
The client asks for its data back
Contracts may require client files to be returned or deleted. Closeout covers guest accounts, shared links and leftover access, with a record of what changed.
Separation of client information
Account protection, device security, sharing reviews and offboarding keep each client’s information apart.
Projects
Separate access by client
Where client material lives in Microsoft 365 or Google Workspace, access is limited to the people assigned to that client. Reviews of external links and inherited permissions catch access beyond the team.
Associates
One contributor leaving should not disrupt the team
Associates and subcontractors use named accounts limited to the work they do. Their sessions and permissions can be removed without touching the rest of the team.
Devices
Device protection for remote work
Enrolled computers get endpoint protection, encryption and security updates, and the controls stay on at home, at a client site or on the road.
Sign-ins
Account-takeover monitoring
Multi-factor authentication (MFA), tight administrator rights and sign-in monitoring make a stolen password much harder to use. Suspicious sessions and new inbox rules are investigated by the security team.
Evidence
Have something to show when a client asks
Reports of completed security work are ready for client questionnaires, proposals, insurance renewals and internal reviews.
Closeout
End access when the project ends
Accounts, active sessions, external links and guest access are reviewed when each project closes.
Evidence for client security reviews
Current records of the security work are ready for procurement questionnaires and questions from existing clients.
- Client procurement
- Do you enforce MFA, encrypt laptops, and remove access when staff leave? Can you show it?
- Policy and coverage reports for MFA, device encryption, and endpoint protection, with offboarding records for recent departures.
- Client IT or security team
- Who monitors your environment, and what can they see?
- Documentation of who can access monitoring tools and which data those tools collect from the systems covered by the service.
- Cyber insurer, at renewal
- Are backups tested? Is sign-in activity monitored? How quickly is access removed?
- What the backup includes and the restore test results, sign-in monitoring records, and the documented offboarding process.
Security for business systems
Protection for Microsoft 365 and Google Workspace, set up around how your firm shares information and who needs access to it.
On Microsoft 365
- SharePoint and OneDrive limited to the team on each client project
- Guest and associate access reviewed when each project closes
- MFA, Conditional Access, and administrator controls
- Managed endpoint protection on supported devices
On Google Workspace
- Shared drives limited to the team on each client project
- External links and guest access reviewed when each project closes
- MFA and administrator access controls
- Admin and sign-in reporting retained as evidence
Settings are kept up to date as part of the service, and upgrades to the tools and monitoring you already have come at no extra cost.
Frequently asked questions.
How are staff access changes handled?
Coverage follows the users and supported devices you choose. New accounts are set up through a documented onboarding process. When someone leaves, the account is disabled, every session is signed out and access is removed for staff, associates and guests. Timing and who does what are settled before the service starts.
Can consultants work securely from client sites?
Yes. Account security policies and managed device protection stay on outside the office. Exact coverage depends on whether the device is enrolled, which sign-in policies your licence includes, and any rules a client network or application sets.
How does the service support insurance applications and renewals?
Insurance reviews match the insurer’s questions to current evidence of the security controls that are running. Every insurer and policy is different, so the evidence supports the application but can’t guarantee approval or coverage.
What happens when a security alert is raised outside business hours?
People on the security team review alerts around the clock and act on the ones that point to a real threat. Before monitoring starts, you agree which systems are covered, what access Teclara has and what the security team may do on its own in an incident.
What support is available for client security questionnaires?
Written evidence covers the controls Teclara runs, such as sign-in policies, device coverage, monitoring, backup, access reviews and response records. The firm stays responsible for its own questionnaire answers, client commitments and any legal or compliance interpretation.
What isn’t included?
The firm stays responsible for its client contracts, questionnaire answers, incident-notification decisions and any commitment to keep or destroy client data. Client systems, project applications, source repositories and other platforms are covered only if you add them.
What a client says about working with us.
“Teclara materially improved both our operational responsiveness and our security posture.”
E.C.
Senior Leadership, GTA Consulting Firm
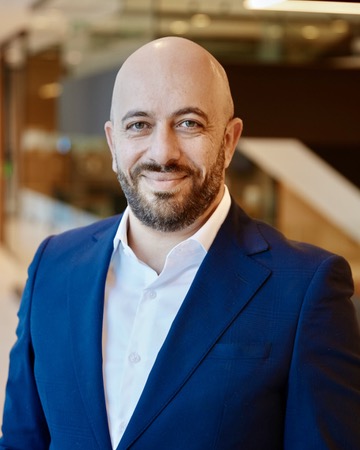
Led by Wadhah Hussain, Teclara's founder
Enterprise Architect · 20+ years in enterprise IT, including OMERS, Accenture, Deloitte and Slalom
Based in Oakville, serving Canada remotely, excluding Quebec.
Work is delivered remotely from Oakville, and there are no offices in the other listed areas.
Your firm’s security, looked after.
Facing a client security questionnaire? A 15-minute call is the easiest place to start.