

Establish security controls that support a growing team
Set clear account, device, and sharing policies early, with documented controls for customer and investor reviews.
Or email hello@teclara.tech
Security risks
Prepare for security reviews as the company grows.
Hiring, enterprise sales, and fundraising introduce new access needs and security questions. Establish consistent controls and keep records as the team grows.
First hires
Define administrator access
Use named accounts and limit administrator privileges to roles that need them. Review access as new employees join and responsibilities change.
First enterprise deal
Procurement sends a questionnaire
Enterprise buyers may require a security review before signing. Current control records help your team provide accurate answers during procurement.
Fundraise
Investors review security practices
Investors may ask about data protection, access controls, and past incidents during due diligence. Maintaining records throughout the year helps your team respond with current evidence.
First departure
Remove access when an employee leaves
An early employee often holds admin rights, shared credentials, and ownership of key accounts. A documented offboarding process transfers account ownership and removes access on the agreed departure date.
Security controls
Early access decisions compound as the team grows
Consistent account setup, device protection, sharing policies, and backup procedures help your team manage security as it grows.
Identity
Limit administrator privileges
Multi-factor authentication, named administrator accounts, and sign-in monitoring protect the tenant. Administrator privileges are limited to roles that need them and reviewed regularly.
Devices
Protect supported laptops and phones
Devices covered by the service receive managed endpoint protection, encryption, and security updates. We document device coverage so your team can identify any gaps.
Sharing
Set collaboration rules deliberately
External sharing, guest access, and link expiry are configured around how the team works. Configuration monitoring helps identify settings that drift as new tools and workflows are added.
Email
Reduce phishing and impersonation
Email controls filter common account-takeover, fake-invoice, and impersonation attempts. Additional domain protection can help prevent impersonation of the startup in outgoing email.
Recovery
Maintain independent cloud backups
Microsoft 365 or Google Workspace mail and files are backed up outside the tenant and tested for recovery.
Evidence
Document the controls in place
Scheduled reports record the controls Teclara operates, current gaps, and assigned actions. The startup uses that evidence when it answers customer, investor, insurance, or audit questions.
Security documentation
Customers, investors, and insurers ask for evidence before a SOC 2 report exists.
While preparing for a formal audit, your team can provide clear descriptions of existing controls and records of their operation.
- Enterprise customer
- Do you have a SOC 2 report? If not, can you complete our questionnaire?
- Answers backed by current reports on MFA, device protection, backup, and access reviews. Teclara does not issue SOC 2 reports; the records support a questionnaire now and an audit later.
- Investors conducting due diligence
- Has the company had a security incident, and how is customer data protected?
- Monitoring and alert handling history, access permissions, and backup coverage for the agreed systems.
- Cyber insurer
- Is MFA enforced for every user? Are backups tested?
- MFA coverage and the backup scope, with the date and result of the last restore test.
Your responsibilities
The startup remains responsible for its diligence answers, contractual commitments, product security, and any certification or audit. Teclara operates and documents the controls we manage. Source repositories, production cloud infrastructure, customer applications, and other SaaS platforms are included only when specified in the service agreement.
Managed Security & Compliance
Ongoing security for your accounts, devices, and data.
The security controls on this page run on the platform you use, with access controls, reporting, and maintenance schedules adapted to your startup.
On Microsoft 365
- MFA and a short list of tenant administrators
- SharePoint and OneDrive sharing configured deliberately
- Managed endpoint protection on supported devices
- Repeatable account onboarding and offboarding
On Google Workspace
- MFA and a short list of super administrators
- Shared-drive and external-sharing defaults reviewed
- Gmail phishing and impersonation protection
- Admin and sign-in reporting retained as evidence
Configuration updates are part of the service. When our security baseline changes, your environment is updated without a separate project fee.
Frequently asked questions.
How does security coverage change as the startup grows?
Coverage is based on the users and supported devices included in your agreement. We follow a documented process to set up accounts for new hires. When staff leave, we disable their accounts, revoke active sessions, and remove access from the systems we manage. Pricing and scope are updated as the environment changes.
How long does onboarding take?
Timing depends on your current cloud setup, devices, licensing, and the issues found during our initial review. We agree on the work and schedule before onboarding begins.
Can you help with investor or customer security reviews?
We provide written evidence for the controls Teclara operates, including sign-in policies, device coverage, monitoring, backup, access reviews, and response records. The startup remains responsible for its questionnaire answers, contractual commitments, product security, and any audit or certification.
What if we already have IT or DevOps staff?
Managed Security & Compliance can work alongside internal IT or DevOps. Responsibilities are documented so the startup knows who handles security alerts, Microsoft 365 or Google Workspace configuration, user support, product infrastructure, source repositories, and other cloud systems.
Do you support remote and distributed teams?
Yes. Account security policies and managed device protection can remain in effect outside the office. The exact coverage depends on whether the device is enrolled, which sign-in policies are licensed, and which systems we manage.
Which systems are included?
The starting point is Microsoft 365 or Google Workspace, supported devices, email security, monitoring, and cloud-tenant backup. Source repositories, production cloud infrastructure, customer applications, and other SaaS platforms require separate scoping.
Client feedback
What a client says about working with us.
“Teclara materially improved both our operational responsiveness and our security posture.”
E.C.
Senior Leadership, GTA Consulting Firm
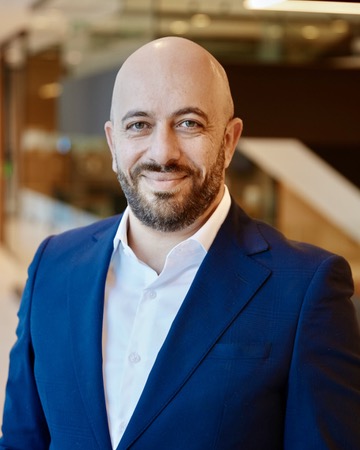
Led by Wadhah Hussain, Teclara's founder
20+ years enterprise IT · Big Four alumnus · Microsoft & Google Cloud specialist
Where we work
We're based in Oakville and work remotely across the region.
Each area page explains how delivery works there. We don't keep offices outside Oakville, so where you're located doesn't limit what we can support.
Short on time? Let your favourite AI sum up Teclara.
Review your security before the next customer assessment
In a 30-minute conversation, we discuss your customer questionnaire, current systems, and deadline. We agree on the next step. Technical checks and written findings belong to a separately scoped engagement.