

Cybersecurity for financial services firms.
Protection for client information across email, accounts and devices, with technical records supporting client, insurer and compliance reviews.
Rather not book now? Leave your email and we'll get in touch.
We reply within 24 hours. Privacy policy
Send a message or email hello@teclara.tech
Security across the client relationship
Client onboarding, payment instructions and advisor departures all change who can see client information. Technical controls keep that access where it belongs.
Onboarding
Clients send their personal documents
Identification, void cheques and statements often arrive as email attachments. Each record is stored where it belongs, and only the right people can open it.
Instructions
A client asks to move money
Attackers impersonate clients or take over mailboxes to send fake transfer requests. Email controls flag many of these messages before anyone acts on them.
Advisor departure
An advisor leaves the firm
When an advisor leaves, their mailbox, client folders and devices hold records that belong to the firm. Access is removed on the planned date, and the mailbox is kept for as long as the firm decides.
Review
Compliance asks for evidence
Dealer reviews, regulatory examinations and partner assessments can ask for records showing how client information was protected over time.
Access and incident records
Records show account activity, the protections that are on, and how each alert was handled in the managed systems.
Identity
Advisor and administrator account protection
Multi-factor authentication (MFA), tight administrator rights and sign-in monitoring make a stolen password much harder to use. Suspicious sessions and new inbox rules are investigated by the security team.
Email
Impersonation and transfer-fraud protection
Email controls filter phishing, fake invoices and impersonation. Changed payment or transfer instructions still need an independent check before money moves.
Access
Client information is only for those who need it
Permissions, external sharing, and administrator roles are reviewed in Microsoft 365 or Google Workspace.
Devices
Work device protection
Supported computers covered by the service get managed endpoint protection, encryption and security updates. The security team reviews alerts, investigates suspicious activity and coordinates the response.
Recovery
Cloud backup and recovery
Microsoft 365 or Google Workspace is backed up every day to a separate location, and restores are tested.
Evidence
Be ready to explain how information is protected
Reports show the protections in place, open gaps and who follows up, ready for client, insurance, audit and regulatory reviews.
Records for external review
What a review asks for depends on the firm’s activities and registration. Current records of the security work are ready to support it.
- Dealer or regulator
- How is client information protected, and would you know if an account were compromised?
- Sign-in monitoring records, access reviews and alert history for the managed systems, with dates and the actions taken.
- Bank or insurer partner
- What controls do you run, and how would you tell us about an incident?
- Control descriptions and evidence for the partner’s third-party risk review, which OSFI Guideline B-10 expects federally regulated financial institutions to carry out.
- Cyber insurer, at renewal
- Is MFA enforced? Are payment-change requests verified outside email?
- MFA coverage and email protection reports. The firm documents its own payment-verification procedure, and Teclara provides evidence of the account and email controls it runs.
Security for business systems
Protection for Microsoft 365 and Google Workspace, set up around how your firm shares information and who needs access to it.
On Microsoft 365
- MFA, Conditional Access, and administrator controls
- SharePoint and OneDrive access reviewed on a schedule
- Managed endpoint protection on supported devices
- Sign-in and sharing records retained for review
On Google Workspace
- MFA and administrator access controls
- Gmail phishing and impersonation protection
- Shared-drive and external-sharing access reviewed
- Admin and sign-in reporting retained for review
Settings are kept up to date as part of the service, and upgrades to the tools and monitoring you already have come at no extra cost.
Frequently asked questions.
What support is available for regulatory and compliance reviews?
Teclara runs and documents technical controls such as sign-in policies, access reviews, endpoint protection, monitoring, backup and response records. Which laws, regulators, frameworks and notification rules apply depends on the firm and its activities. Teclara doesn’t certify compliance or replace legal and compliance advisers.
What evidence is available for insurance applications?
Insurance reviews match the insurer’s questions to current evidence of the security controls that are running. Every insurer and policy is different, so the evidence supports the application but can’t guarantee approval, coverage or a claim outcome.
How are potential incidents handled?
People on the security team review alerts around the clock and act on the ones that point to a real threat. What the team can do to contain an incident depends on the systems covered and the actions you approved in advance. Legal, regulatory, client and insurance notifications stay the firm’s decision, made with its advisers.
What can be recovered after ransomware or deletion?
Backed-up Microsoft 365 or Google Workspace data can be restored to an earlier point once the threat is contained in the affected accounts or systems. How long recovery takes depends on what was hit, how much data there is and what comes first. Portfolio, CRM, trading, policy, local-server and custodian systems need their own recovery plans.
Is security awareness training included?
Yes. Managed Security & Compliance includes ongoing awareness training and safe phishing tests. Training helps staff spot impersonation, fake invoices and payment-change scams, alongside the technical controls and the firm’s own payment checks.
What isn’t included?
The firm decides which laws, regulators, contracts and notification rules apply. Teclara doesn’t certify compliance or replace legal, compliance, insurance or regulatory advisers. Portfolio, CRM, trading, policy and custodian systems, other business applications and local servers are covered only if you add them.
What a client says about working with us.
“Teclara materially improved both our operational responsiveness and our security posture.”
E.C.
Senior Leadership, GTA Consulting Firm
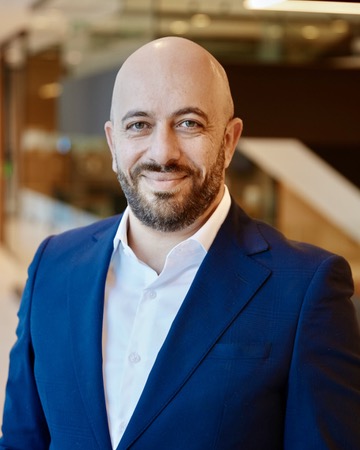
Led by Wadhah Hussain, Teclara's founder
Enterprise Architect · 20+ years in enterprise IT, including OMERS, Accenture, Deloitte and Slalom
Based in Oakville, serving Canada remotely, excluding Quebec.
Work is delivered remotely from Oakville, and there are no offices in the other listed areas.
Your firm’s security, looked after.
Not sure what your next review will ask for? A 15-minute call is an easy place to start.