

Protect brokerage email and reduce payment fraud risk
Secure the email accounts used by agents and administrators, protect client records, and monitor for suspicious sign-ins and forwarding rules.
A 30-minute conversation about your setup, priorities, and next step. Technical checks and written findings are scoped separately.
Send a message or email hello@teclara.tech
Security risks
Protect communications at each stage of a transaction.
Agents exchange client information and payment instructions with buyers, lawyers, and lenders. Account protection and independent payment verification help reduce the risk of fraudulent instructions.
Offer accepted
Deposit instructions go out
A fraudulent follow-up can replace legitimate deposit instructions with different banking details. Payment changes should be verified through a trusted contact method.
Before closing
Lawyers and lenders join the thread
Attackers may impersonate lawyers or lenders in a transaction. Email controls help detect impersonation, while monitoring identifies suspicious inbox-rule changes that could hide replies.
Every deal
Identity records are collected
FINTRAC requires brokerages to verify client identity and keep the records. Those files need controlled access and a backup that has been tested.
Agent moves
An agent changes brokerage
Remove access to brokerage email, files, and shared links when an agent leaves, following the agreed offboarding schedule.
Security controls
Payment fraud often starts before the instructions change
An attacker with mailbox access can read transaction details and use them to make fraudulent payment instructions more convincing. Sign-in monitoring and email controls help identify suspicious activity.
Email
Reduce phishing and impersonation
Email controls filter common fake-instruction, invoice, and impersonation attempts. Additional domain protection can help prevent impersonation of the brokerage in outgoing email.
Sign-ins
Watch for account takeover
Multi-factor authentication, administrator controls, and sign-in monitoring help prevent unauthorized access using stolen credentials. The security team investigates suspicious sessions under the agreed response process.
Mail flow
Review forwarding and inbox rules
Unexpected forwarding and inbox rules can hide replies or copy a conversation elsewhere. The security team monitors rule changes and investigates suspicious activity.
Devices
Protect supported brokerage devices
Managed endpoint protection, encryption, and security updates apply to supported devices covered by the service.
Access
Remove agent access promptly
Named accounts, active sessions, guest access, and shared links are reviewed when an agent or administrator leaves.
Recovery
Define backup coverage for brokerage data
We maintain independent backups of Microsoft 365 or Google Workspace data and test restores. Brokerage, transaction, CRM, and legal systems run by other providers need their own backup and recovery arrangements.
Security documentation
Retain the records needed to investigate suspicious email.
Sign-in and email logs help investigators assess whether a message came from a compromised account or an impersonated sender. The available evidence depends on the platform and its log-retention settings.
- A client, after a fraud attempt
- Did that email with the new banking details come from your agent?
- Available sign-in logs, mailbox-rule history, and message-trace records help establish how the email was sent. Findings depend on the records retained by the platforms involved.
- FINTRAC examination
- Can you produce the identification and transaction records you are required to keep?
- Permission reports and backup records for the systems storing those files.
- Cyber insurer, at renewal
- Is MFA enforced for every agent? Is email protected against impersonation?
- MFA coverage across agent accounts, email protection and domain authentication status, and device coverage.
Your responsibilities
The brokerage remains responsible for FINTRAC compliance and for independently verifying changes to deposit, payout, or closing instructions using a trusted channel. Teclara operates the account, email, device, sharing, and backup controls we manage. Brokerage, transaction, CRM, legal, and personal-device systems are included only when specified in the service agreement.
Managed Security & Compliance
Ongoing security for your accounts, devices, and data.
The security controls on this page run on the platform you use, with access controls, reporting, and maintenance schedules adapted to your brokerage.
On Microsoft 365
- MFA and administrator controls for brokerage accounts
- Forwarding and inbox-rule changes monitored
- Managed endpoint protection on supported devices
- Agent access reviewed during offboarding
On Google Workspace
- Gmail phishing and impersonation protection
- Forwarding and filter changes monitored
- Shared-drive and external-sharing access reviewed
- Agent access reviewed during offboarding
Configuration updates are part of the service. When we upgrade the tools and monitoring in your agreement, you get the upgrade at no added cost.
Frequently asked questions.
How can payment redirection begin in email?
An attacker with access to a mailbox can read transaction details and send fraudulent payment instructions. An impersonated sender can also request payment changes. Sign-in monitoring, email filtering, forwarding-rule review, and staff training reduce that exposure. The brokerage should still verify payment changes independently using a trusted channel.
Are we exposed if the lawyer handles the funds?
Brokerage staff may still participate in the email conversation or pass payment instructions between the parties. Security controls around those accounts matter even when another party moves the funds. The brokerage and its lawyer remain responsible for their own verification, legal, insurance, and regulatory procedures.
Can you protect agents using personal devices?
Account and sign-in controls can apply regardless of device ownership, subject to platform licensing and policy. Endpoint protection, encryption, and device-level response apply only to supported devices that are enrolled. Personal devices outside management remain outside endpoint coverage.
What happens when an agent leaves?
During offboarding, we can disable accounts, revoke active sessions, and remove guest access and shared links from the systems we manage. Timing and responsibility are agreed with the brokerage in advance. Removing brokerage data from an unmanaged personal device depends on the controls that were configured before departure.
Can you help with a cyber insurance application or renewal?
Yes. We review the insurer’s questions and provide current evidence for the security controls we manage. Requirements vary by insurer and policy, so the work supports the application but does not guarantee approval, coverage, or a claim outcome.
Client feedback
What a client says about working with us.
“Teclara materially improved both our operational responsiveness and our security posture.”
E.C.
Senior Leadership, GTA Consulting Firm
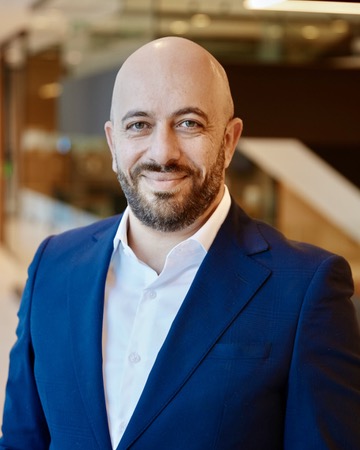
Led by Wadhah Hussain, Teclara's founder
Enterprise Architect · 20+ years in enterprise IT, including Big Four consulting
Where we work
Based in Oakville. We work remotely with firms across Canada.
Each area page explains how delivery works there. We don't keep offices outside Oakville, so where you're located doesn't limit what we can support.
Review email security and agent access
In a 30-minute conversation, we discuss agent access, payment instructions, and client information. We agree on the next step. Technical checks and written findings belong to a separately scoped engagement.